
@somecat cementary for the living

@woozle [pets cementery]
Discussion
Logging took the trees that bears called home. The Haida Nation is building them new dens: https://cheknews.ca/logging-took-the-trees-that-bears-called-home-the-haida-nation-is-building-them-new-dens-1352366/
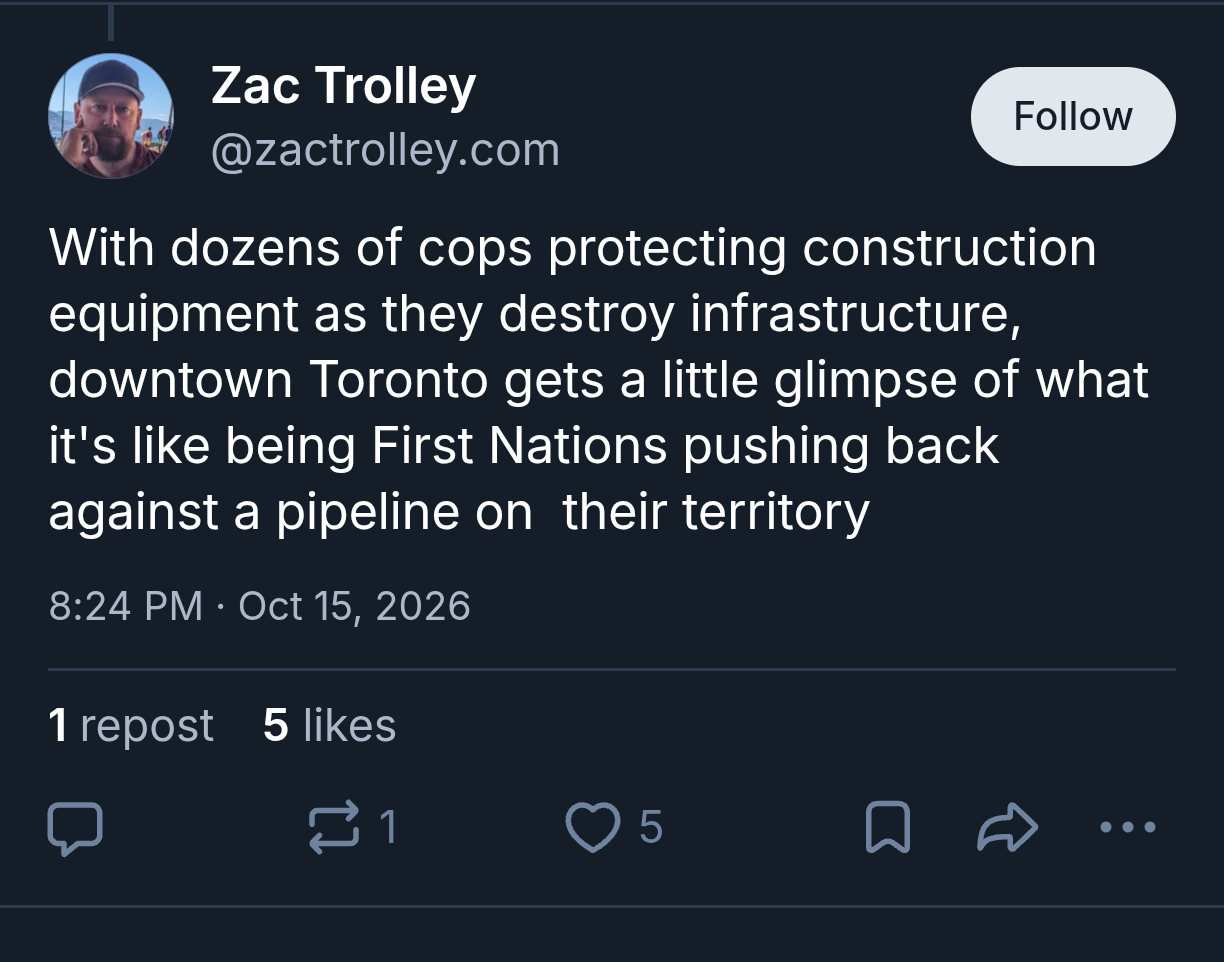
In response to Desmond Cole's video for The Breach, which points out that Doug Ford's war on Toronto bike lanes is part of a global right wing fossil fuel led push back against climate actions, Zac Trolley makes an interesting comparison to First Nations pushing back against pipelines:
https://breachmedia.ca/doug-ford-bike-lanes-removal/
#TheWarOnCars #BikeTO #Toronto #OnPoli #ClimateChange #FossilFuels #Fridays4Future
It's been sixteen years since we started "The Architecture of Open Source Applications" project (https://aosabook.org/). I'm occasionally tempted to put together another volume, but what I'd actually rather do is have people write a chapter each describing the architecture of what they'd build if they could start from scratch today. What would your ideal package manager look like? How would you structure the internals of a modern shell? In another timeline…
#WritersCoffeeClub – 16th Oct. How do you feel about people reading your works without buying a personal copy?
Long-standing publishing lore is, there are roughly four readers per book sold. This includes library loans, second-hand sales, and friends borrowing books. This is normal.
I don't get mad at warez sites (most downloads go unread, most readers wouldn't have bought one), but I *DO* get enraged by pirates who re-list and sell my ebooks on amazon (they're stealing income from authors).
@cstross Reminds me of an online discussion I had with an author a few years back: he wasn't selling well, and complained (in jest... maybe) that he wasn't even on any pirate sites. Not being an author myself, I don't know which would feel worse: having your works pirated, or not read at all.
If you don't know where to start, a great starting point would be:
Good luck!
2/2
RE: https://tech.lgbt/@nina_kali_nina/117441043503225633
The new policies for the Linux kernel make it more or less impossible to support a slop-free fork of Linux, so if you're worried about the reliability of your system level software, or have ethical concerns about LLM usage on your computer, the time to act is, well, now.
If you have time this weekend, I recommend you to try one of the slop-free systems: NetBSD, 9front, HyperbolaBSD, Haiku, or OpenBSD. If you're adventurous, you could try new AlpineBSD, or research smaller systems, like FreeDOS. If you don't feel adventurous, you might want to check out anti-AI Linux distributions, like Elementary or Gentoo.
There's no "one solution that fits all". But there's a solution that I chose for myself, and that's NetBSD: it gives me the most freedom, it supports most of my hardware, and can run a great deal of software I need. It's not easy to run, but it's a great learning opportunity. There's quite a few folks around using BSD and capable of giving hints and advice, so if you feel stuck, toot about #netbsd.
1/2
@rey Should I fediblock?
@woozle no, it's the European Union's instance, they've just been taken over by fash
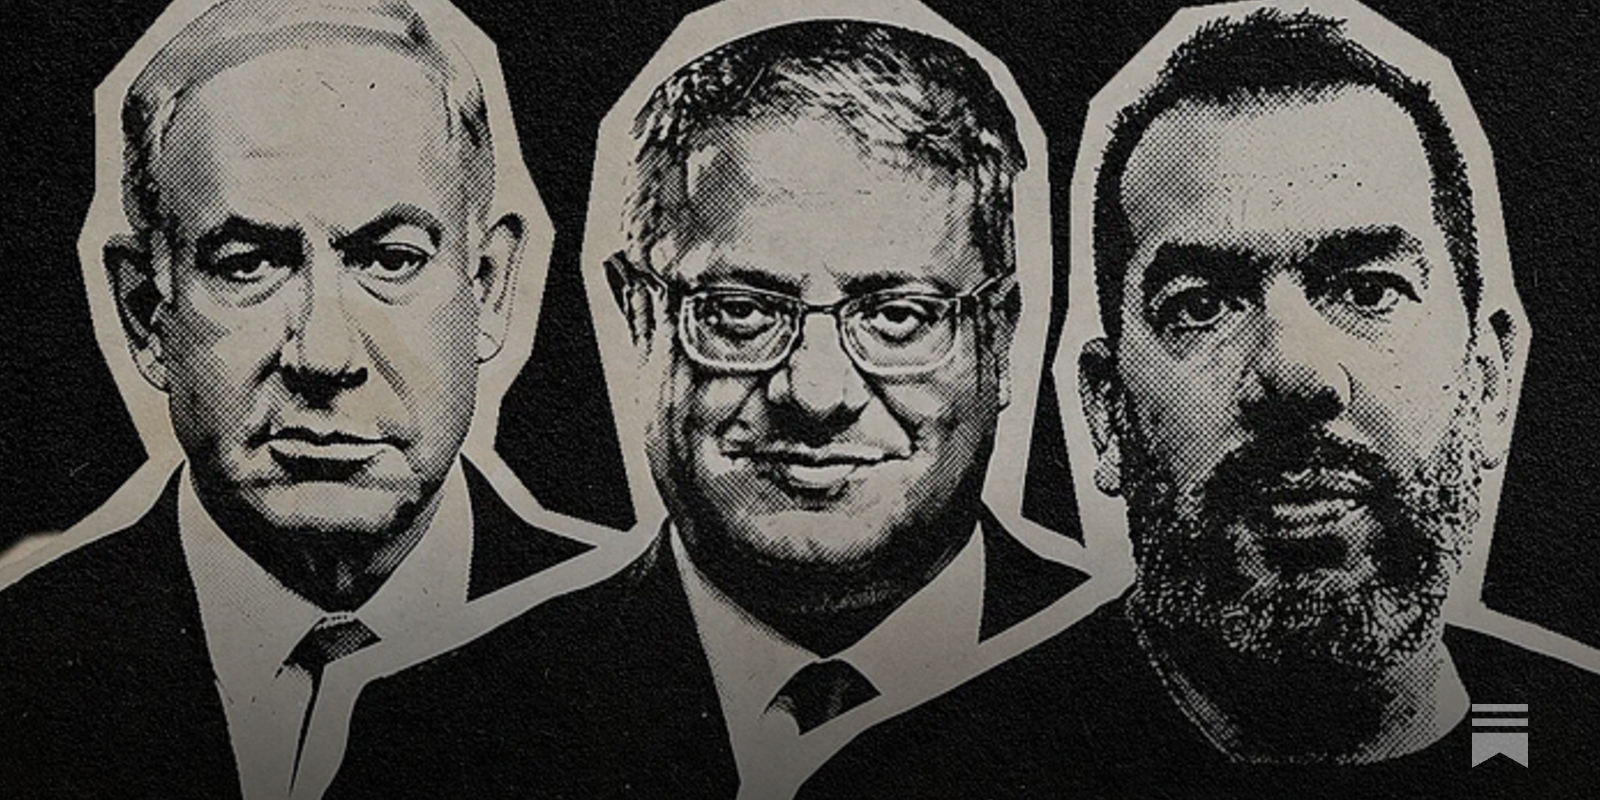
"Brazil’s far right has long had ties to the Netanyahu administration. Israeli flags are a common sight at Bolsonaro rallies. Benjamin Netanyahu has referred to Jair Bolsonaro as his brother. The Bolsonaro sons make regular trips to Israel, and Carlos Bolsonaro was investigated for setting up a parallel intelligence agency to spy on political opponents and journalists in partnership with the Israeli surveillance company Pegasus.
One of Flávio’s campaign promises is to strengthen ties with Israel.
Israeli Prime Minister Benjamin Netanyahu publicly supports Flavio Bolsonaro in this year’s Brazilian presidential election.
Israeli political strategist Nevo Cohen has publicly said he is working on an election campaign in Brazil. For example, in June, he wrote, “I got back this week from an election campaign in Brazil,” while commenting on the Brazilian and Israeli elections."
Read more: https://www.panamericandispatch.org/p/far-right-israeli-strategist-confirms
#Brazil #elections #netanyahu #bolsonaro #FuckIsrael #farright #politics
One thing we’ve decided: when we leave for our getaway we are adopting alternate identities. We’ve already come up with new names. Now we’re working on our story.
I’m thinking we are a notorious team of international jewel thieves. Always one step ahead of Interpol.
Of course that’s complicated because then we have to have yet another alternative identity that’s the public cover for our true criminal career. Maybe we are luxury bagel entrepreneurs?
@impermanen_ You want *two* new identities. One to be the safer one, and then one sympathizably bad one if they discover you're not really the first one.
You could be bat guano collectors (it's what one of my ancestors did in central America).
@quixoticgeek Buffer overflow
Linus is saying the quiet part out loud: AI-native projects are environments where the key ingredient is _capital_. Abstraction can be performed by a quiet appreciation. True automation can be disruptive.
AI-based architectures (again, assuming that the AI works reliably, which is a highly contingent proposition) translate all that stuff into capital flows. A "machine speed" project requires _money_ to participate in, regardless of their complexity.
Ok, looks like this is the week of funny experiences.
Customer: "I had an AI check our server and it says the SSH port is open and that's not very secure."
Me: "Yes, you asked us to open it so you could access the server via SFTP (actually, you wanted FTP, but we discussed it a bit and found this compromise). Don't worry, it's only accessible from your IP and you land in a dedicated FreeBSD jail. From there, you can only access the 'exchange' directory on your server, where you can upload and download files without affecting the application."
(NB: I had suggested a VPN, but they declined because it was too complicated.)
Customer: "Yes, but maybe it's still insecure. Can't we close it?"
Me: "No, unless you want to lose access to that directory."
Customer: "Ok, thanks."
One hour later:
Customer: "Hi, I think we've found a solution. We've just created an app (!!!) with AI that lets us access the files anyway, but more securely than SSH (!!!). Can we install that and close SSH? Oh, and not in the dedicated jail, but directly in the application's jail, because it needs access to the application's files."
Me: "Frankly, I trust SSH in a dedicated jail, restricted by the firewall, a lot more. I don't think this is a good idea."
Customer: "Ok, thanks."
Half an hour later:
Customer: "Ok, now it's secure. I had another AI check it and it found some security issues, but it fixed them all. Can you install it and disable SSH?"
Me: "I strongly advise against it. I can see problems coming."
Customer: "Ok, thanks."
One hour later, my phone rings.
Their internal IT guy (who has access to the machine, which, after all, belongs to them) had given the AI the login credentials to go ahead with the operation.
Except the AI had managed to lock itself out via the firewall, without even starting the app. And now they couldn't get back in.
Fortunately, I had my own access, via VPN, to a separate jail that the AI hadn't touched (or even considered).
Customer: "SORRYSORRYSORRYSORRYSORRY! From now on, we do things your way."
Well, at least it ended well.
PS: The customer knows I'm sharing this story and agreed to it.
@stefano
LLM is leverage, it won't solve poor user.
I don't understand why the customer didn't trust professional developer in this story
Everyone can tell you used AI to do it. They just aren't saying anything about it because they want to be polite.
(Do you know someone who needs this thought to pop unbidden into their head?)
@futurebird I am in Germany right now and noticed that commercial ads and flyers do have a little label "made with AI". Seems to be a new EU law. Very helpful in deciding which stores to avoid.
Sitting by the window watching the rain come down. Cup of tea in my hand.
@melaniebartos behält man da bei euch den SSO Account wenn man abschließt, oder ist man seinen Fedi Account dann los und kann zumindest einen "Nachfolger" angeben?
@stefan Den Uni-Account ist man los, aber das Fediverse nicht: Zum Glück haben wir die Portabilität und können auf eine andere Instanz umziehen. Dabei helfen wir auch gerne weiter seitens der Moderation der Instanzen.
Sorry, the app encountered an unexpected error

Install bonfire.cafe
Get the full app experience